Business Email Compromise Reports to NCUA Rose From 27 to 40. It Is the Only Comparison in the Report.
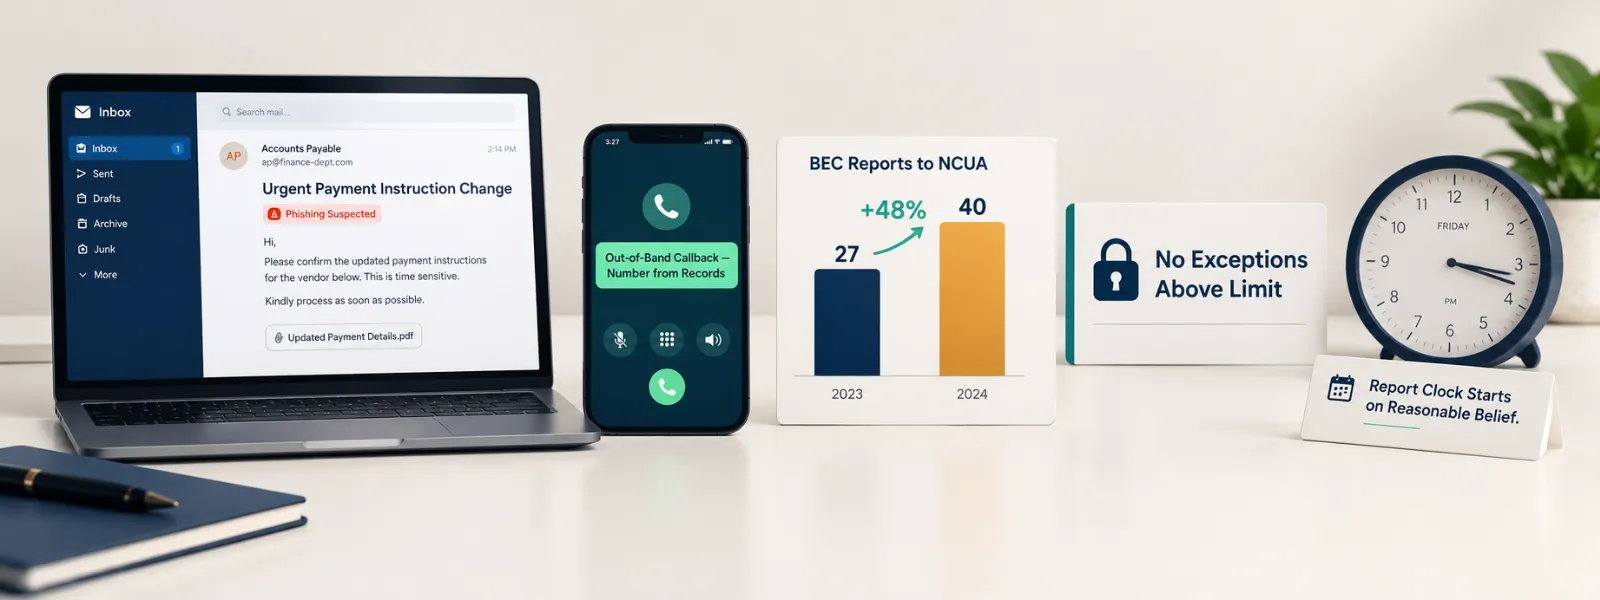
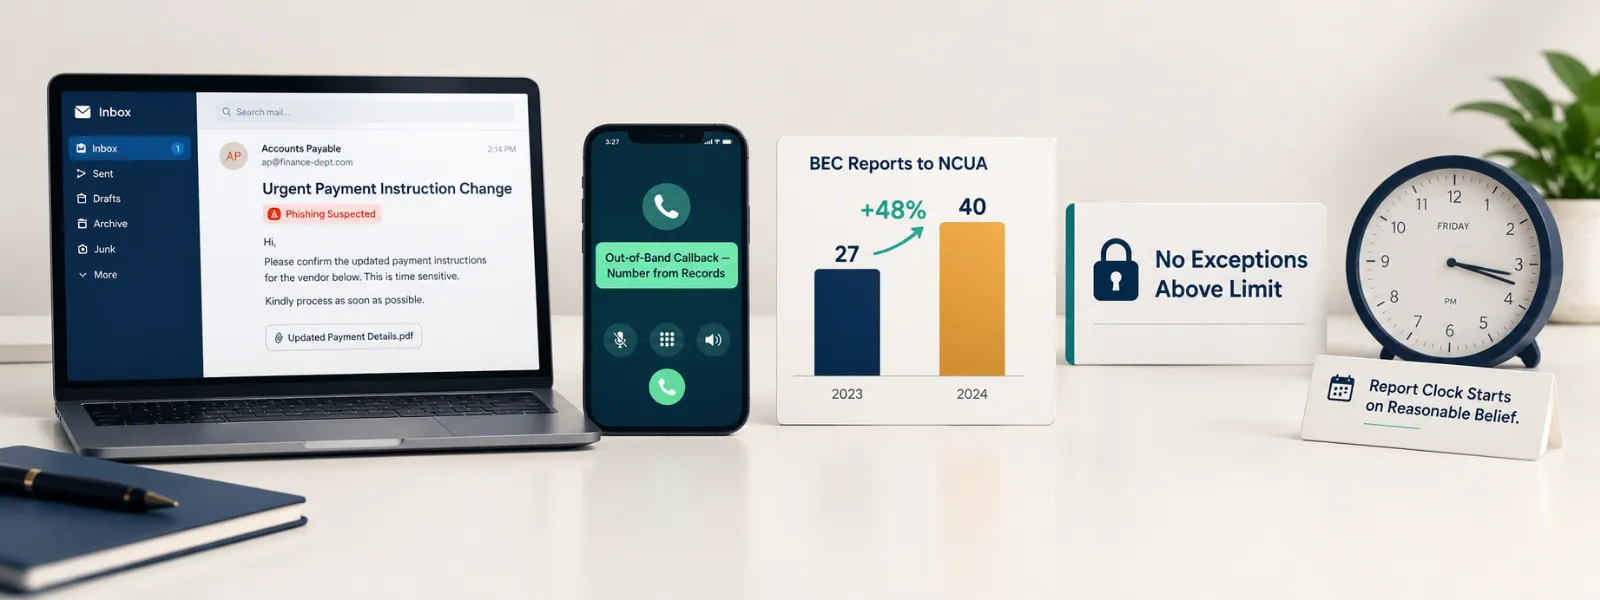
NCUA's 2026 Cybersecurity and Credit Union System Resilience Report gives one year-over-year comparison for a specific attack type. Forty known instances of business email compromise were reported by credit unions between May 1, 2025 and April 30, 2026, against 27 in the prior reporting period.
That is a 48 percent increase on a small base, and it is the only category in the report where NCUA published both periods.
Total reported cyber incidents moved from 539 to 588 over the same comparison. So BEC grew faster than the overall total, and its share of reported incidents went up.
The absolute numbers deserve care. Forty is described as known instances reported to NCUA. Incidents that were caught before loss, handled without a report, or never identified as BEC do not appear. Treat the direction as the signal and the magnitude as a floor.
Why this category is different from the rest of the threat list
The 2026 report lists six current and emerging threats: AI-enabled attacks, business email compromise, quantum and cryptographic risk, ransomware, state-sponsored activity, and third-party risk.
Five of those are largely about technical controls, vendor posture, or geopolitical conditions you do not influence. BEC is about a payment leaving your institution because a person believed an instruction.
NCUA's own framing notes that BEC is not unique to financial services and remains a prevalent means of intercepting payments, citing the FBI's Internet Crime Complaint Center on its financial damage.
The control that stops it is not primarily an email control. It is a verification step in the payment process, and it is one you already own.
The 40 versus 27 comparison is the most useful number in the 2026 report for an operational conversation, because it is the only one that is both directional and tied to a control you can change this quarter. Everything else in the threats section describes conditions. This one describes an outcome with a known countermeasure.
What the report says is making it worse
NCUA devotes the most space in the threats section to AI, and links it directly to the social engineering that drives BEC.
The report attributes to CrowdStrike's 2026 Global Threat Report a finding that attacks involving AI-enabled techniques increased by nearly 90 percent. It describes threat actors combining multiple data sources including social media to build tailored phishing, and using AI after an intrusion to map organizational relationships toward financial fraud or extortion. It notes that agentic capabilities reduce the need for human involvement, letting attackers work at greater scale.
Two qualifications. The 90 percent figure is NCUA citing a vendor threat report rather than publishing its own measurement. And the mechanism described, better-targeted pretexting at higher volume, is an intensification of an existing attack pattern rather than a new one.
The practical implication is unchanged by either qualification. If your BEC defense depends on staff noticing that a message looks wrong, the quality of the messages is improving faster than the training cycle.
When a BEC becomes a reportable incident
The February 2023 NCUA final rule requires a federally insured credit union to notify NCUA within 72 hours of a reportable cyber incident. The trigger is reasonable belief that one has occurred, not confirmation, and NCUA's guidance treats notification received from a third party that data has been compromised or operations disrupted as starting the clock.
The definition covers an incident that results in a substantial loss of confidentiality, integrity, or availability of a network or member information system through unauthorized access or exposure of sensitive data, disrupts vital member services, or causes a serious impact on the safety and resiliency of operational systems and processes.
A BEC that moves money without touching a system may or may not meet that definition depending on the facts. A BEC that began with a compromised mailbox is a different analysis, because unauthorized access occurred.
The practical answer is to make that determination a named step in your BEC response with an owner, rather than a judgment someone makes after the money is gone.
What to do this quarter
Move the control from detection to verification. Out-of-band callback on any payment instruction change, using a number from your records rather than from the message. This is the single control that survives a convincing pretext, because it does not require anyone to judge whether the message was genuine.
Set a dollar threshold and a no-exceptions rule above it. The failure pattern in most BEC losses is an exception granted under time pressure by someone senior enough to grant it. A documented threshold with no override authority removes the decision from the moment.
Test it against your own executives. Tabletop a request that appears to come from your CEO, to a member of your finance team, on a Friday afternoon, with urgency. You are testing whether the verification step actually runs when the social pressure is real, not whether people can identify a phishing email in training.
Extend the same rule to vendor payment changes. Your third parties are a path in. A vendor risk assessment that covers data security but says nothing about how that vendor authenticates a change to its own remittance details leaves the gap open.
Check what your reporting trigger actually is. The 72-hour notification under 12 CFR Part 748 runs from reasonable belief that a reportable cyber incident occurred, not from confirmation. A BEC loss discovered on a Friday does not wait for Monday's investigation to start the clock.
Source note
This article is based on NCUA's 2026 Cybersecurity and Credit Union System Resilience Report, published June 2026 and last modified September 25, 2026, including its current and emerging threats section and its reported incident figures; the 2025 report published April 2026; and NCUA's cyber incident notification requirements at 12 CFR Part 748. The 48 percent figure is arithmetic on the 40 and 27 counts NCUA published. The CrowdStrike figure and the FBI Internet Crime Complaint Center characterization are reported here as NCUA cited them and have not been verified against the underlying sources.
Disclaimer
This article is provided for general information and does not constitute legal advice. Regulatory requirements, compliance dates, examiner priorities, and enforcement posture change frequently. Incident counts described here are reports received by NCUA and are not a measure of total incident volume. Verify current requirements against primary agency sources and your legal counsel before acting on anything described here.